Exabeam’s Security Management Platform (SMP) allows security teams to outsmart the odds by adding intelligence to their existing security tools. Out-of-the-box use case coverage delivers repeatable outcomes, greatly reducing burnout for understaffed and overwhelmed security teams who are already stretched thin.
With organizations rapidly increasing their cloud consumption in the age of remote work, The Exabeam SMP allows organizations to detect improper access of cloud storage objects and defend against threats to cloud-based data on AWS, Google Cloud and Microsoft Azure.
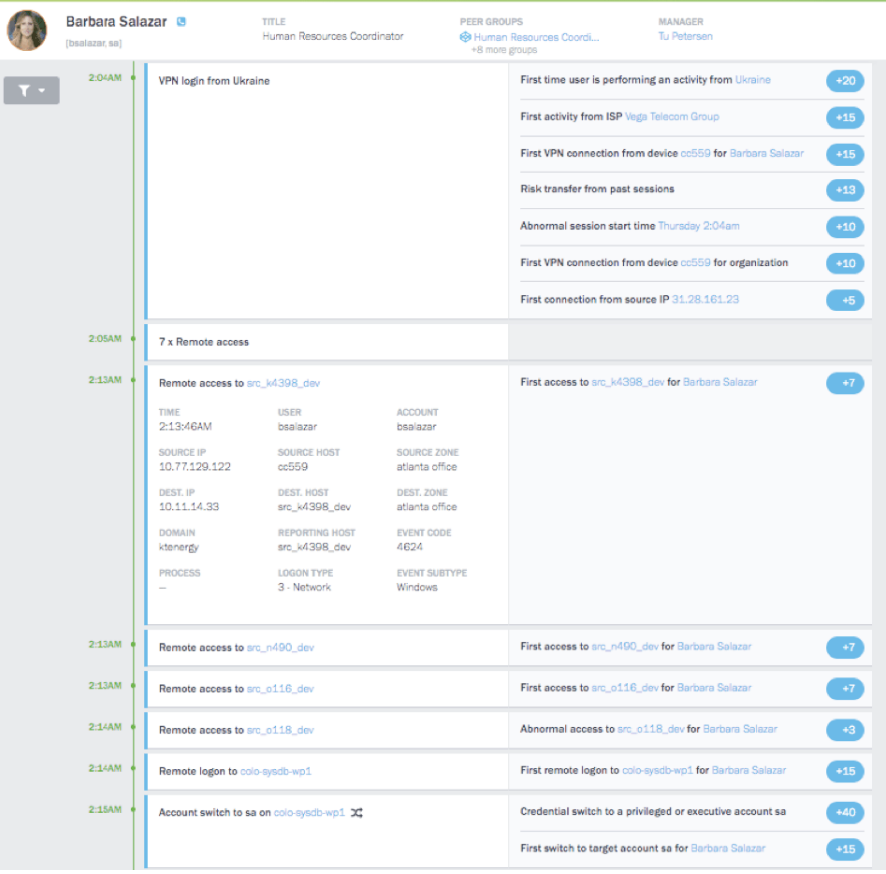
Insider threats typically go under the radar due to the threat actor posing as a legitimate user. The Exabeam SMP provides real-time mapping of logs to attribute behavior to users and devices. With data enhancement and context, security teams have visibility into abnormal behavior and risky activity to stop insider threats.
In traditional SIEMs, investigations can consume upwards of 70% of analyst time. The Exabeam SMP includes automation that reduces the time it takes analysts to detect, triage, investigate and respond to incidents by 51%, including automated connectors to cloud resources, out-of-the-box detection rules and models, automated timeline creation, behavioral threat hunting, response actions and turnkey playbooks.
The Exabeam SMP includes all of the modern SIEM components – a cloud data lake; user and entity behavioral analytics (UEBA); and security, orchestration and automated response (SOAR) – to help organizations stay as secure as possible.
The Exabeam SMP can be deployed on cloud infrastructure, as software-as-a-service or through a managed security service provider as well as on-premises, helping organizations accelerate their transition to the cloud securely.
About this category: Security Information and Event Management (SIEM)
The Cybersecurity Excellence Awards recognize security information and event management platforms. The category covers products that collect security events, correlate them to detect threats and support investigation and compliance.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
Related categories
View the category →How entries are judged →