The cybersecurity industry is undergoing a shift – once focused on prevention and protection, organizations now want a detection-first posture for cyber defense. In response, the Network Detection and Response (NDR) category has emerged, providing greater visibility for the enterprise. NDR provides detection and response across the three main pillars of the attack surface: on-premises (data centers and remote sites), the cloud, and the edge, including IoT.
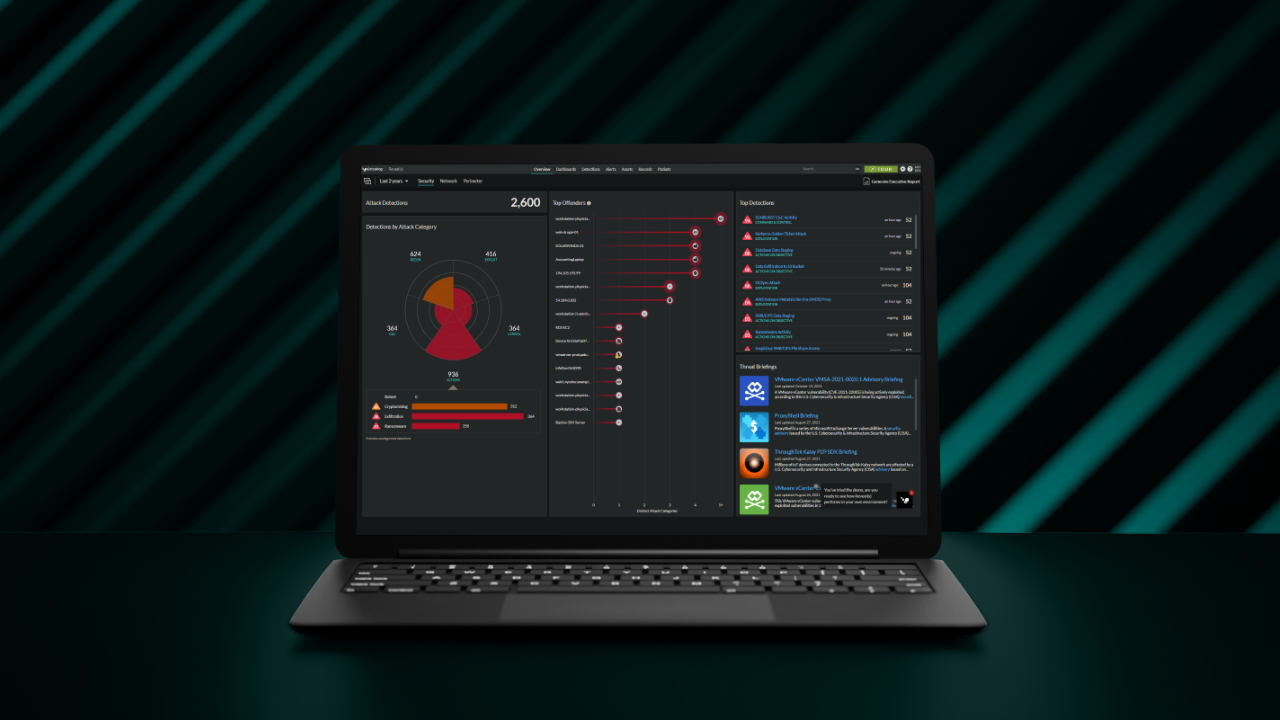
Reveal(x) 360 is the first and only SaaS-delivered NDR solution to provide unified and complete visibility. It applies cloud-scale AI to petabytes of traffic per day, performing line-rate decryption and behavioral analysis across all infrastructure, workloads, and data-in-flight. With complete visibility from ExtraHop, enterprises can detect malicious behavior, hunt advanced threats, and forensically investigate any incident with confidence.
Reveal(x) 360 is also able to identify asset types and functions with a great degree of detail, including gleaning device criticality based on behavior analysis, and gathering information including:
– Which operating systems are in use on each device, and what role each device plays
– Which users have logged in, or attempted to log in to each device
– Which, if any, EDR agent is installed on the device
These capabilities enable Reveal(x) 360 to compare behavior within and across peer groups of devices. For example, if a single conference room phone starts to exhibit behavior that no other conference phone has exhibited, that will be flagged as suspicious. Comparing suspicious behaviors among peers, and understanding whether an attack is primarily targeting IoT devices or some other category or role group, helps analysts understand the scope of an attack and accelerate their response and mitigation activities.
How we are different
Decryption. ExtraHop is the only NDR provider that securely decrypts network traffic, according to the Gartner Market Guide for NDR. When network and cloud traffic are decrypted and analyzed in real time, Reveal(x) 360 is able to expose the more accurate, full spectrum of risks and eliminate blind spots with complete coverage. Reveal(x) 360 monitors all traffic at line rate, gleaning valuable information from SSL and TLS encrypted traffic. Competitors either don’t decrypt or rely on headers to identify encrypted traffic, leaving enterprises open to SQL injection and cross-site scripting attacks. Reveal(x) 360 can then perform full stream reassembly for complete contextual visibility into all transaction payloads from Layer 2 to Layer 7 for over 70 enterprise protocols. Others merely scan the surface, while Reveal(x) 360 drills down deep.
Forensics. ExtraHop is the only NDR provider with the ability to look back 90-days to assess the “blast radius” for critical CVEs, exploits, and zero days. New in-product Threat Briefing reports include comprehensive information about the threat and highlight potentially vulnerable devices on the network. They also include detections associated with and recommended remediation actions for incidents like the REvil (Kaseya) ransomware campaign and Microsoft’s PrintNightmare vulnerability. These help security teams know the impact footprint which in turn drives a decisive incident response process.
Scalability & Visibility. Scalability and visibility are real problems for many network security products. Reveal(x) 360 provides an unparalleled level of scalability and deep insight in threat detection which can analyze a sustained 100 Gbps of traffic in real time, several times more than its leading competitors. Reveal(x) 360 is the only cloud-native NDR solution, allowing users to gain exceptional visibility across their hybrid, on-premises, and remote/work-from-home systems and users in a single interface accessible through an internet browser.
About this category: Network Detection and Response (NDR)
The Cybersecurity Excellence Awards recognize network detection and response products. The category covers products that analyze network traffic to detect threats and support response.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
Community Choice voting for the 2022 season closed on July 10, 2022.
What is the Community Choice Award?
A separate award decided by public vote, independent of the jury awards. Each completed share of a profile on LinkedIn, Facebook or X counted as one vote.
2027 award season
Nominations closeFebruary 27, 2027
Jury winners announcedWeek of March 22
Community Choice voting closesJuly 10, 2027
Nominate in this category
Enter a nomination in Network Detection and Response (NDR). Review takes about one business day.
Help This Nominee Win a Community Choice Award Vote by sharing this page:
2
Community
Votes
Cast your vote by sharing this nominee’s profile on LinkedIn, Facebook, or X, using the buttons above. Each completed social share adds one Community Choice vote.
Votes cast by July 10, 2027 will determine the Community Choice winners (independent of the jury awards). Winners will be announced before Black Hat USA.
What is the Community Choice Award? →
Community Choice is a separate award track from the jury-selected Cybersecurity Excellence Awards. Jury winners are chosen by expert judges, while Community Choice winners are determined by public voting. A nominee may be honored by the jury, the community, or both.
2022 winners in Network Detection and Response (NDR)
To keep judging fair, each entry is judged against peers in its segment, so a category can have more than one Gold winner.