Keysight Threat Simulator is a Breach and Attack Simulation (BAS) platform that enables SecOps teams to safely attack themselves, identify gaps, and fix vulnerabilities before attackers can exploit. Threat Simulator helps security teams continuously validate their defenses and safety.
Boasting an array of real-world threats and exploits, turnkey SIEM integrations, and 24/7/365 updates from Keysight’s Application Threat Intelligence (ATI) Research Center, Threat Simulator empowers SecOps teams to take control of a rapidly changing attack surface.
Threat Simulator sends relevant, targeted attacks from an untrusted zone to container-based software agents deployed within protected zones. With automated scheduling, SecOps teams can regularly assess network security solutions, such as Next Generation Firewalls, Web Application Firewalls, and Data Loss Prevention tools.
Drawing from Keysight’s 20+ year industry leadership in application and security testing, Threat Simulator features an array of real-world attacks and exploits, including:
• malware campaigns
• spearphishing campaigns
• data exfiltration
• cross-site scripting
• malware
• database exploits
• advanced persistent threats
During the stages of a simulated attack, Threat Simulator logs whether established security solutions can thwart the attack and the stage at which it was stopped. Should any stage of the attack succeed, Threat Simulator provides product-specific remediation techniques for SecOps teams to thwart future attacks.
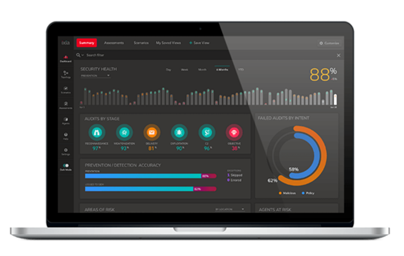
For simplified deployment and cost-effectiveness, Threat Simulator is a SaaS-based platform that shows vulnerabilities, audit statuses, and security measurements over time, and includes a “Security Score” summarizing how secure a network is at any given time based on the number of successful audits.
Keysight’s ATI Research Center continuously updates Threat Simulator with the latest threats and exploits. With continuous updates, SecOps teams can trust they are always ahead by emulating the newest attacks or drilling down into attack signatures and evidence of malicious activity. With Threat Simulator, SecOps teams can take control of a rapidly changing attack surface.
About this category: Adversarial Exposure Validation (AEV)
The Cybersecurity Excellence Awards recognize adversarial exposure validation products. The category covers products that prove whether exposures can be exploited by running safe, automated attacks, such as breach and attack simulation and automated penetration testing.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
Related categories
View the category →How entries are judged →