LogicHub Extended Detection and Response (XDR) is a unified platform that centralizes and simplifies security operations by integrating all security tools, automatically analyzing all security data, and delivering deep threat detection and confirmed cases faster and more accurately than a human analyst.
Unlike vendor-specific closed XDR platforms, LogicHub XDR integrates with any best-of-breed security platform, ensuring that customers are using the solutions that work best for their operating and requirements and budgetary scope.
LogicHub has based its platform on expertise automation and a blend of expert systems with deep neural net architecture, designed to work with a reduced amount of data. The engine progressively learns and updates its own logic to make more accurate decisions like a human analyst. The playbook thus helps in event triage by automating the decision on criticality of events by scoring each event.
LogicHub’s XDR meets critical gaps in detection and response from legacy SIEM, UEBA, and SOAR solutions. For security teams that suffer from alert fatigue, a lack of available skilled resources, and a history of tools that have failed to effectively improve detection and response capabilities, LogicHub XDR provides a highly automated, AI-powered platform that delivers intelligent decision automation, increases detection accuracy through scalable automated playbooks, and continuously hunts for new and advanced threats.
This advanced solution can be deployed as a platform or delivered as a fully managed detection and response service. LogicHub XDR includes:
• Comprehensive integration for cloud, endpoint, network, and user protection
• Automated threat detection and alert triage
• Intelligent decision automation with confirmed threat notification
• Continuous threat hunting
• Fully automated, one-click, and ad hoc incident response actions
• Comprehensive case management
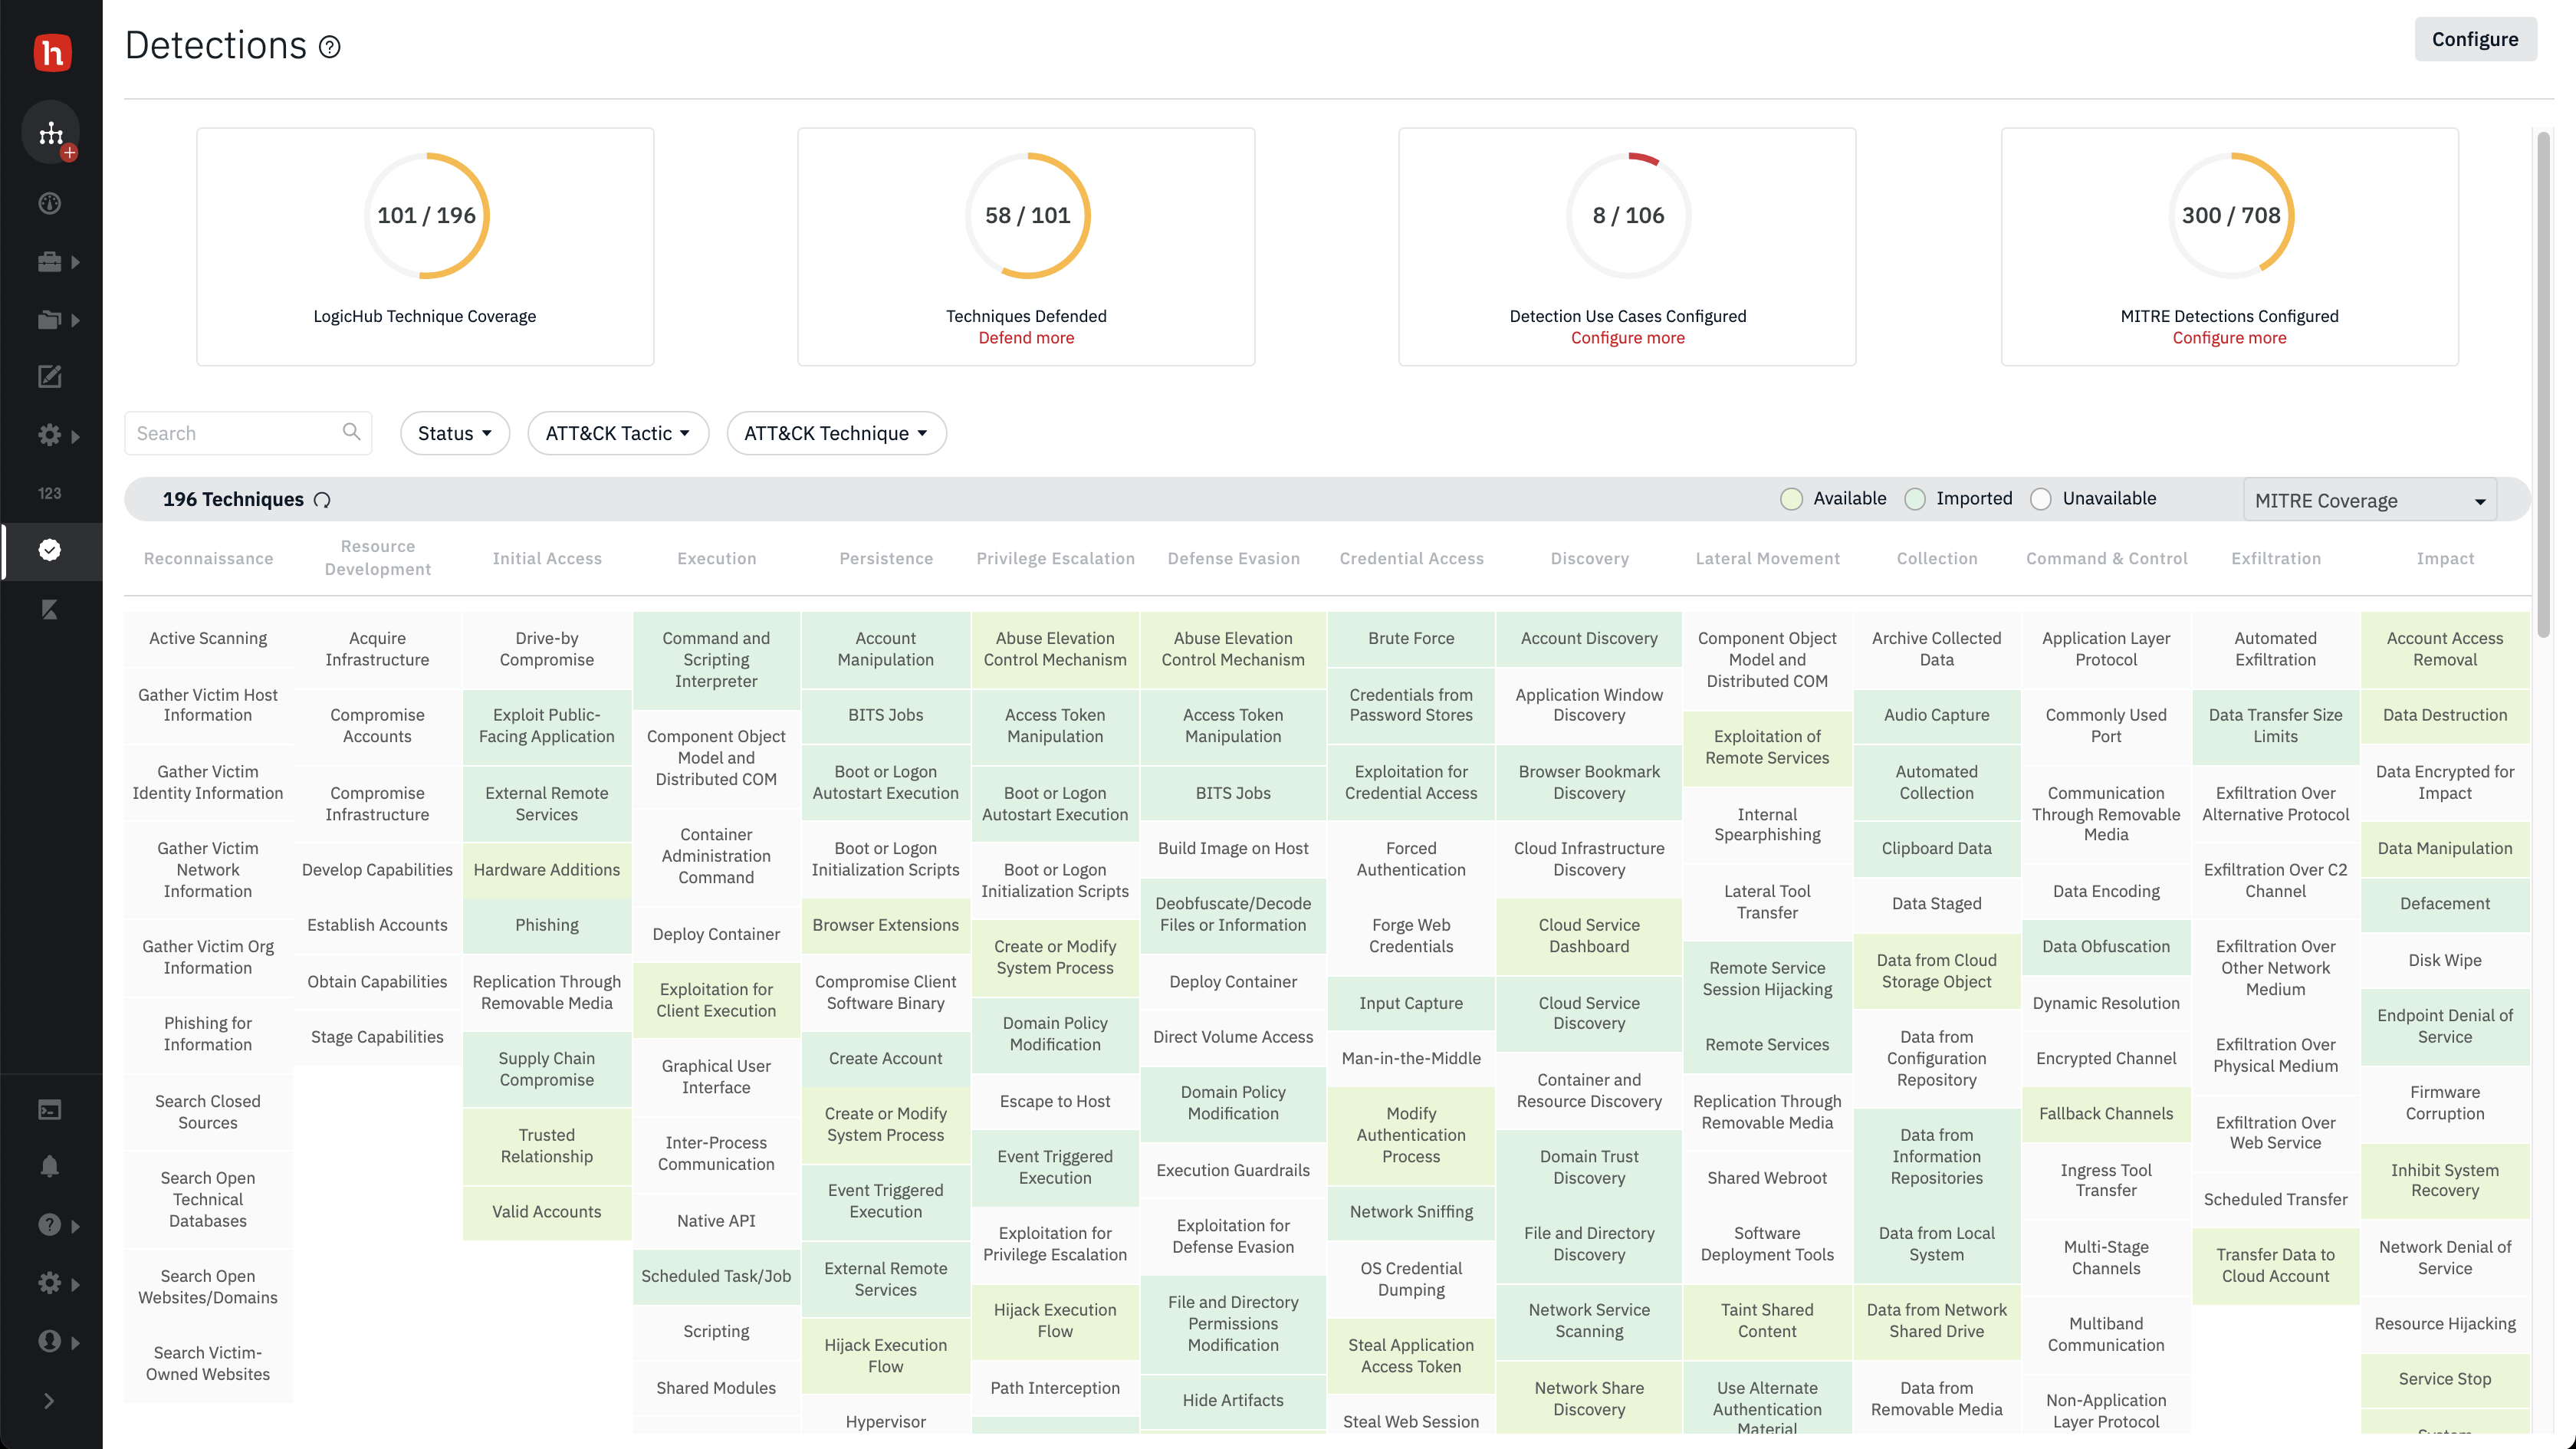
• MITRE ATT&CK framework mapping
• Complete visibility with powerful reporting and dashboards
How we are different
• The LogicHub XDR platform leverages advanced AI and intelligent decision automation to analyze millions of security events per day from any source to detect and hunt threats, triage alerts, and respond with consistent precision at machine speeds and machine scale.
• AI threat detection progressively learns from data and analyst feedback. Skilled human threat hunters can encode their techniques, expertise, and decision processes and turn them into scoring and decision playbooks unique to their organization or use LogicHub’s extensive playbook library.
• LogicHub XDR is vendor-agnostic and offers deep integration with an organization’s entire security stack, working with any best-of-breed security platform to provide a single pane of glass for security operations teams.
About this category: Extended Detection and Response (XDR)
The Cybersecurity Excellence Awards recognize extended detection and response platforms. The category covers products that join detection and response across security layers such as endpoints, network, cloud, identity and email in one platform.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
Community Choice voting for the 2022 season closed on July 10, 2022.
What is the Community Choice Award?
A separate award decided by public vote, independent of the jury awards. Each completed share of a profile on LinkedIn, Facebook or X counted as one vote.
2027 award season
Nominations closeFebruary 27, 2027
Jury winners announcedWeek of March 22
Community Choice voting closesJuly 10, 2027
Nominate in this category
Enter a nomination in Extended Detection and Response (XDR). Review takes about one business day.
Help This Nominee Win a Community Choice Award Vote by sharing this page:
11
Community
Votes
Cast your vote by sharing this nominee’s profile on LinkedIn, Facebook, or X, using the buttons above. Each completed social share adds one Community Choice vote.
Votes cast by July 10, 2027 will determine the Community Choice winners (independent of the jury awards). Winners will be announced before Black Hat USA.
What is the Community Choice Award? →
Community Choice is a separate award track from the jury-selected Cybersecurity Excellence Awards. Jury winners are chosen by expert judges, while Community Choice winners are determined by public voting. A nominee may be honored by the jury, the community, or both.
2022 winners in Extended Detection and Response (XDR)
To keep judging fair, each entry is judged against peers in its segment, so a category can have more than one Gold winner.