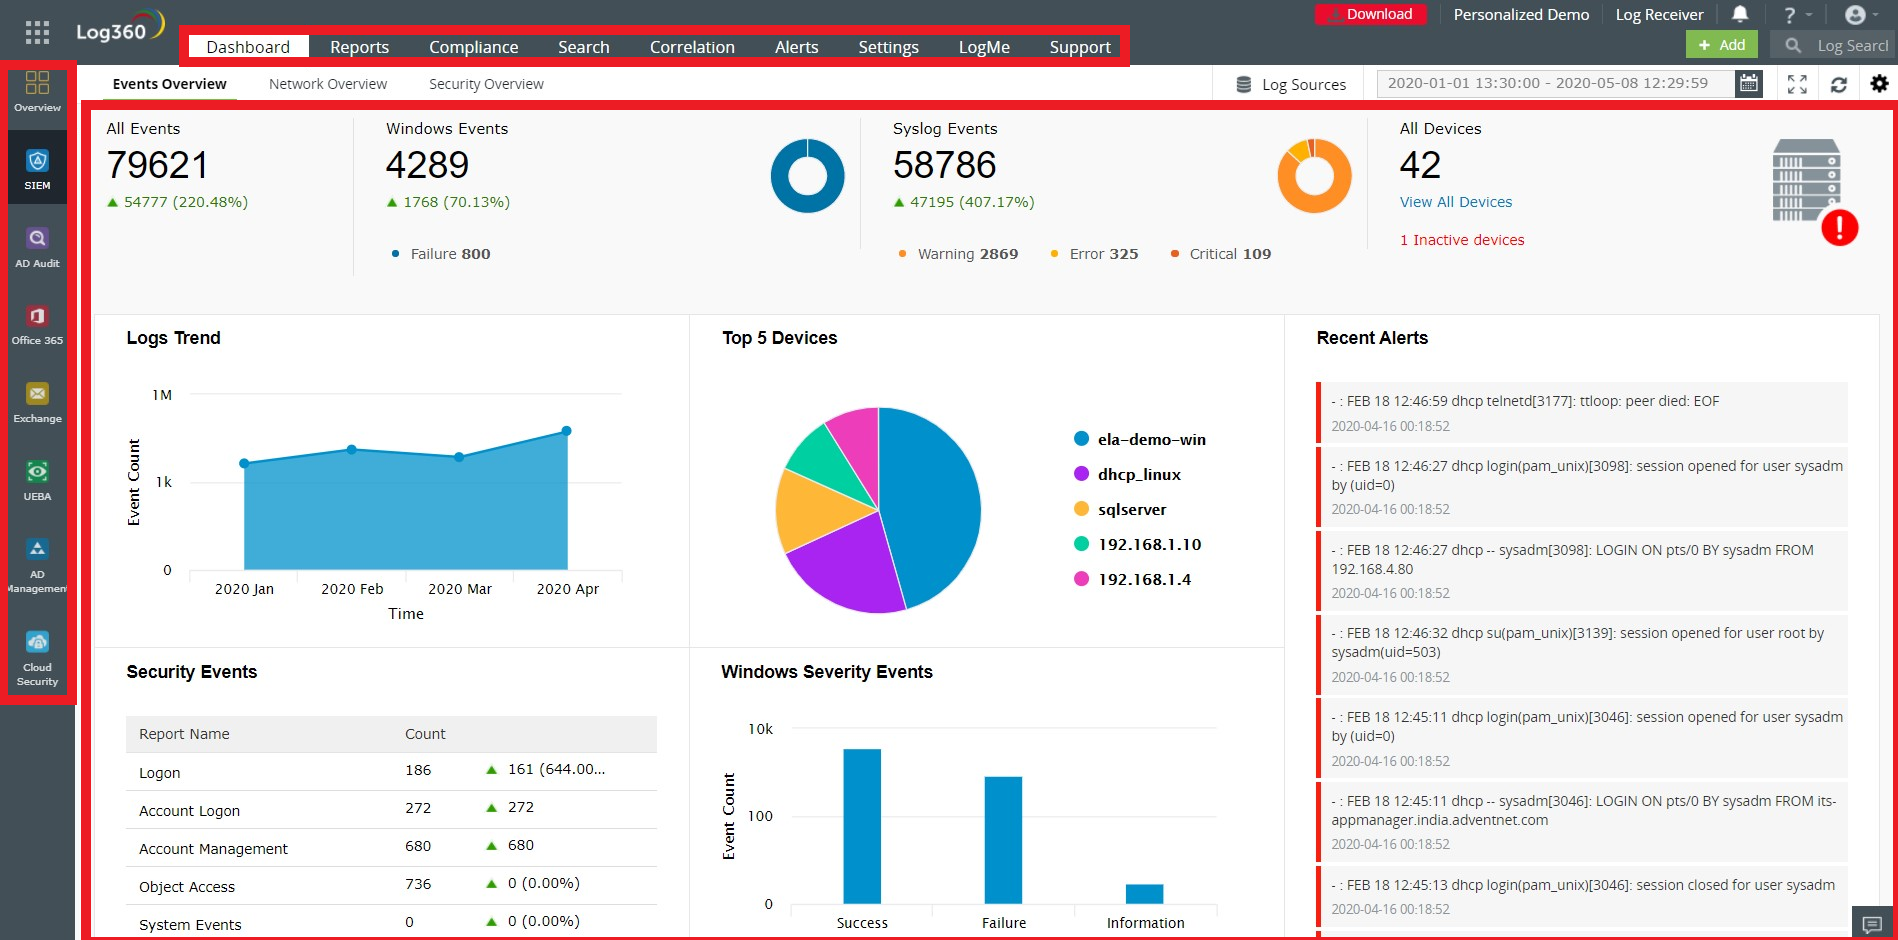
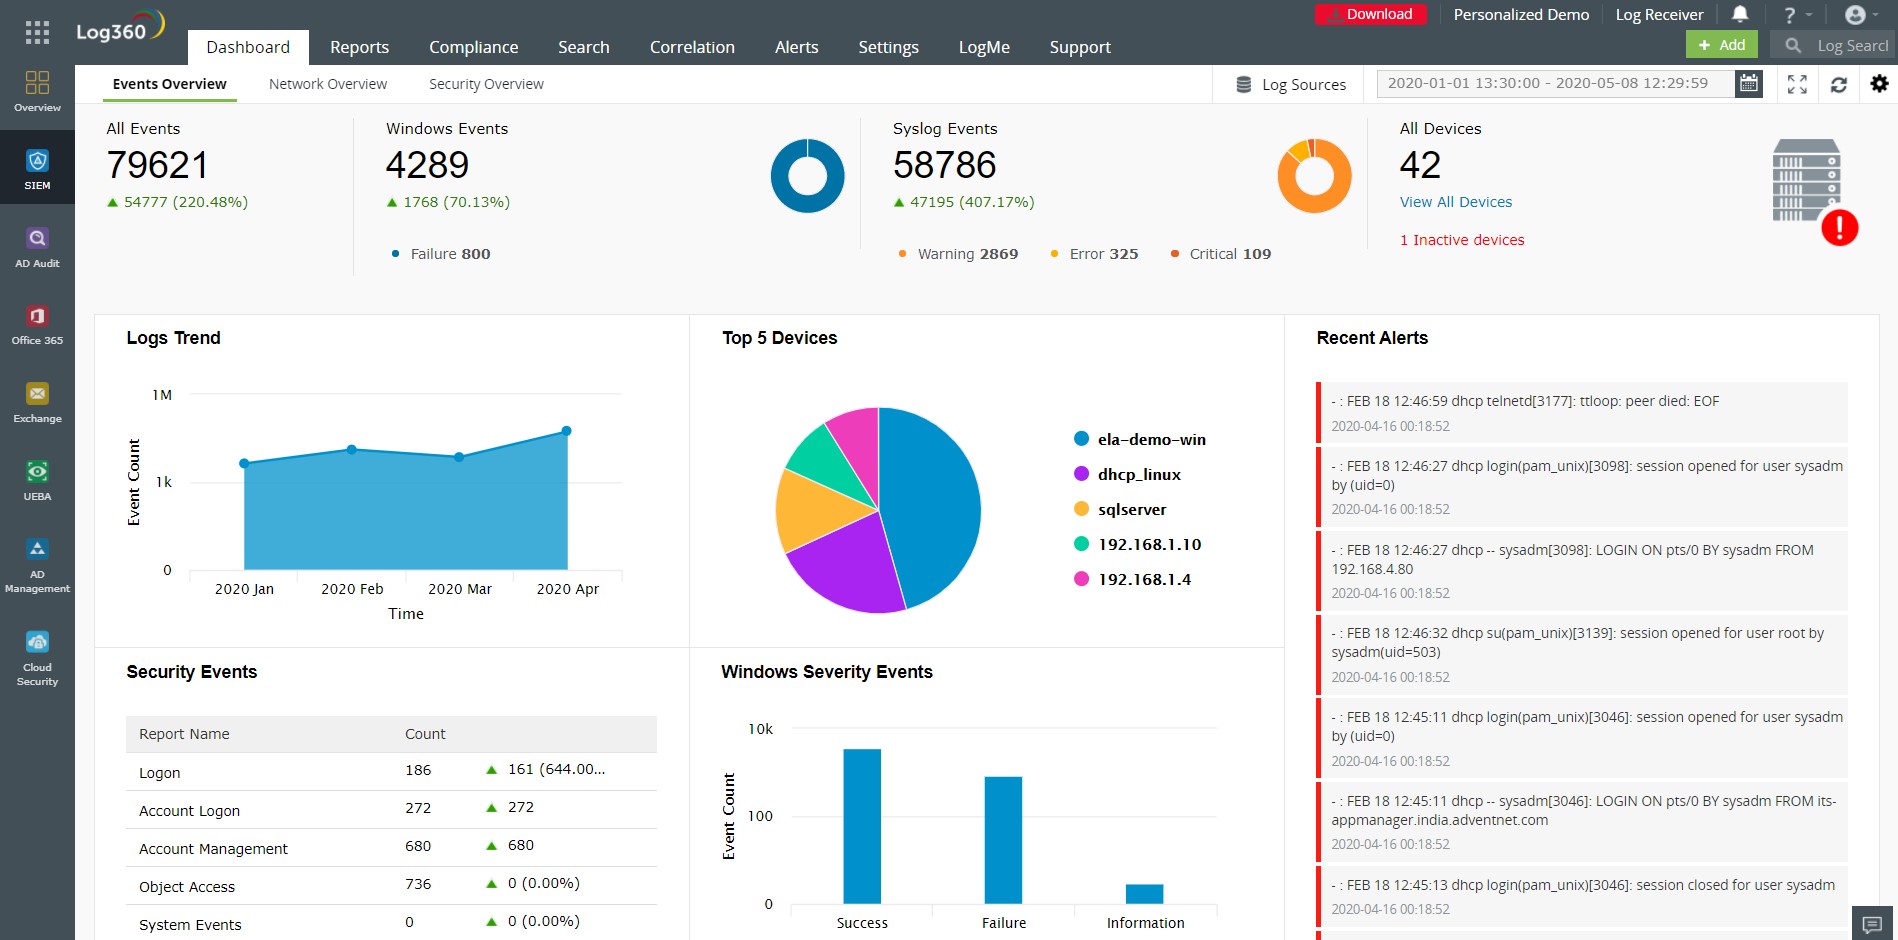
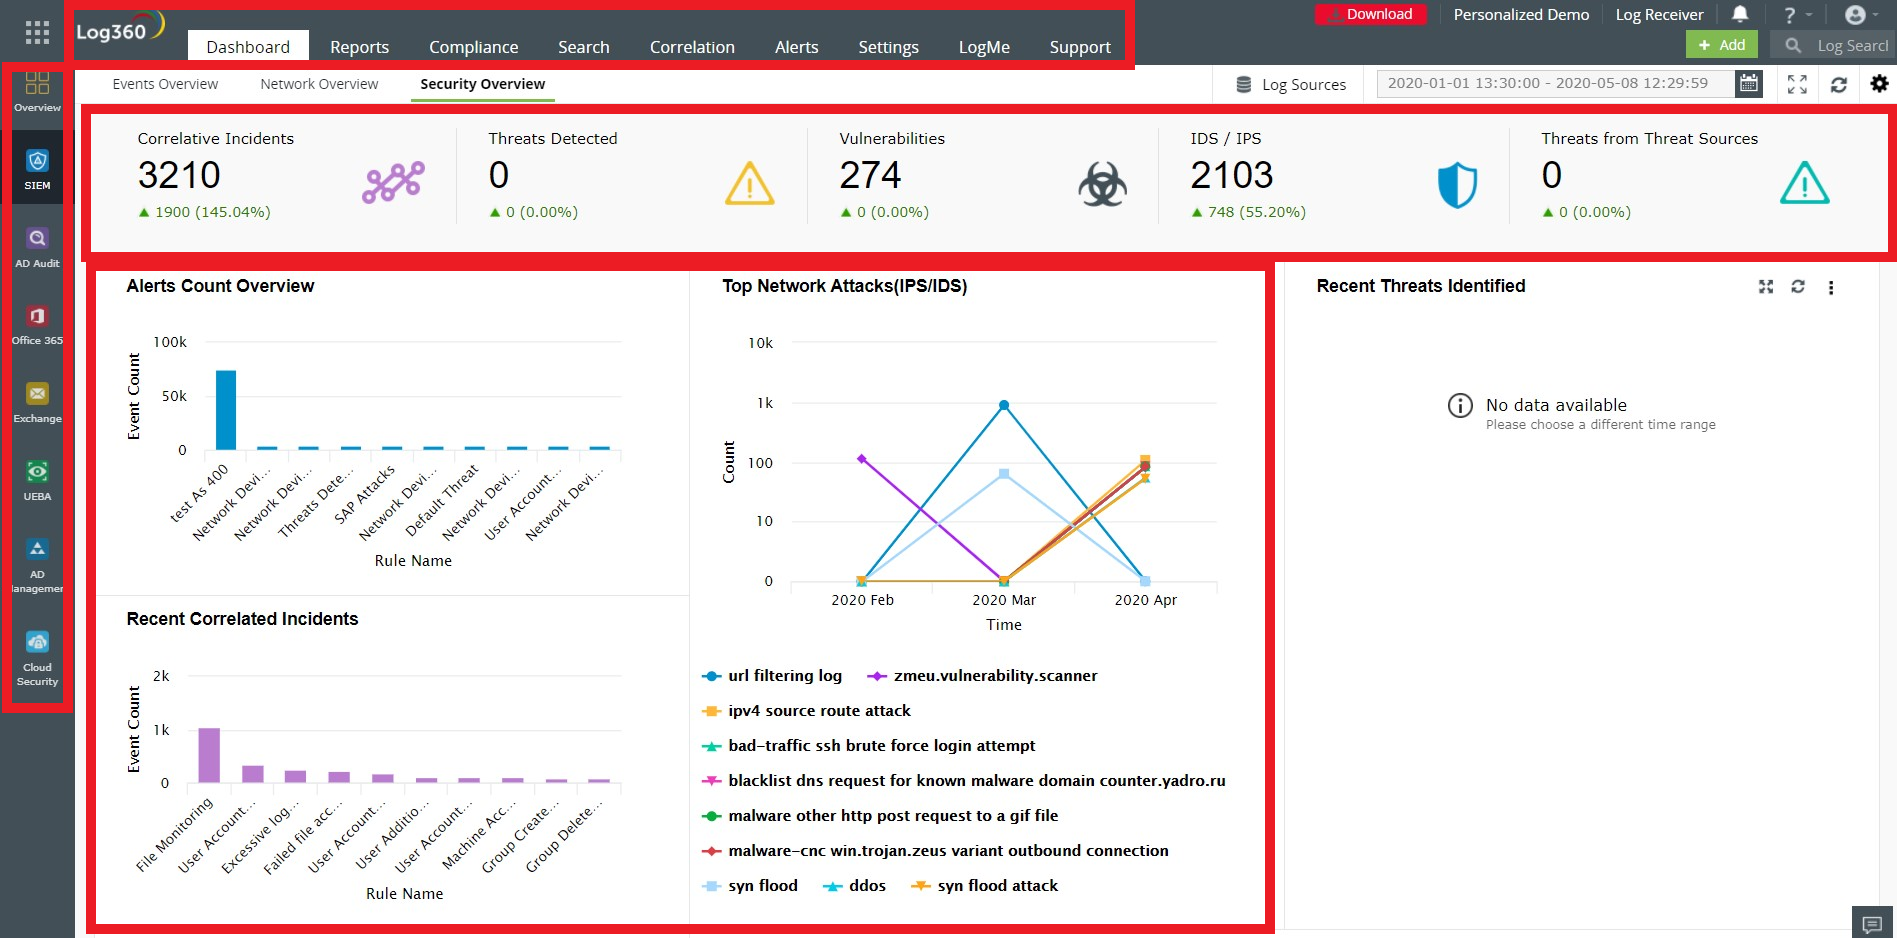
Log360 is a unified SIEM solution with integrated DLP and CASB capabilities to detect, investigate, and respond to security threats. With Log360, you can improve the productivity of your SOC.
Several capabilities from a single console: Network infrastructure security, data security, log forensics, anomaly detection using machine learning algorithms, compliance management, threat intelligence, cloud monitoring, a CASB, user and entity risk analysis, and incident detection and resolution.
1. Data ingestion from over 750 types of log sources: This includes Active Directory, network devices, databases, workstations, endpoint solutions, data loss prevention systems, vulnerability scanners, applications, and cloud services. Organizations can also parse logs from custom applications.
2. Security analytics: Insightful and actionable security analytics are provided for activities that happen in every part of the network. Analytics are logically arranged so that it is easy to find them. Users can also configure alerts based on unique security use cases.
3. Incident response: You can configure workflows and playbooks for mitigating incidents. The solution can be integrated with various third-party help desk and ticketing tools. Technicians can be assigned incidents automatically using rules, and the incident resolution status can be tracked continuously.
4. Correlation of events: The correlation engine enables users to put together seemingly unrelated events from across the network and classify them as potential threats. Built-in correlation rules are provided within the solution along with the option to build custom correlation rules.
5. Anomaly detection: The anomaly detection engine within Log360 can spot behavior abnormalities in users and hosts in a network. Based on the extent of abnormal deviation, a risk score is assigned to every entity. This helps IT teams focus on the most pressing threats first and decreases the number of false positives. There are also options available to customize risk scoring and build your own anomaly models.
About this category: Security Information and Event Management (SIEM)
The Cybersecurity Excellence Awards recognize security information and event management platforms. The category covers products that collect security events, correlate them to detect threats and support investigation and compliance.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
Related categories
View the category →How entries are judged →