Historically, incident detection and response solutions require security professionals to parse through hundreds of trivial alerts, manage an ever-growing mountain of data, and manually forward information from endpoints. In addition, these antiquated detection tools require investigators to have both log search expertise and incident response experience in order to retrace user activity across the network, endpoint, and cloud.
In February 2016, Rapid7 launched InsightIDR to specifically solve these problems, giving security professionals the visibility and confidence they need to move with purpose when suspicious activity is detected.
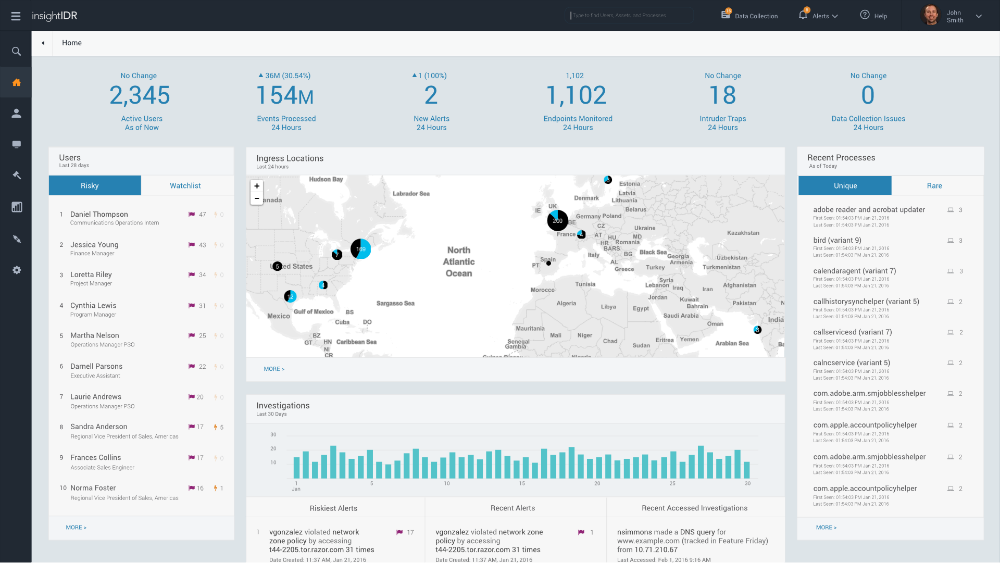
InsightIDR helps find unknown threats with User Behavior Analytics (UBA) and automated deception technology, provides SIEM capabilities to prioritize where to look, and combines the above with Endpoint detection and visibility to leave attackers with nowhere to hide. Customers report that their investigations are 20 times faster, as they can bring together real-time log search, user activity, and endpoint data in a single solution.
InsightIDR, running on a unique multi-tenant cloud architecture, comes with pre-packaged analytics and incident detections to deliver insight quickly. Security professionals are able to spend less time managing their security data, benefiting from fast search, constantly updated detections and the comfort that their log data is outside the hands of attackers.
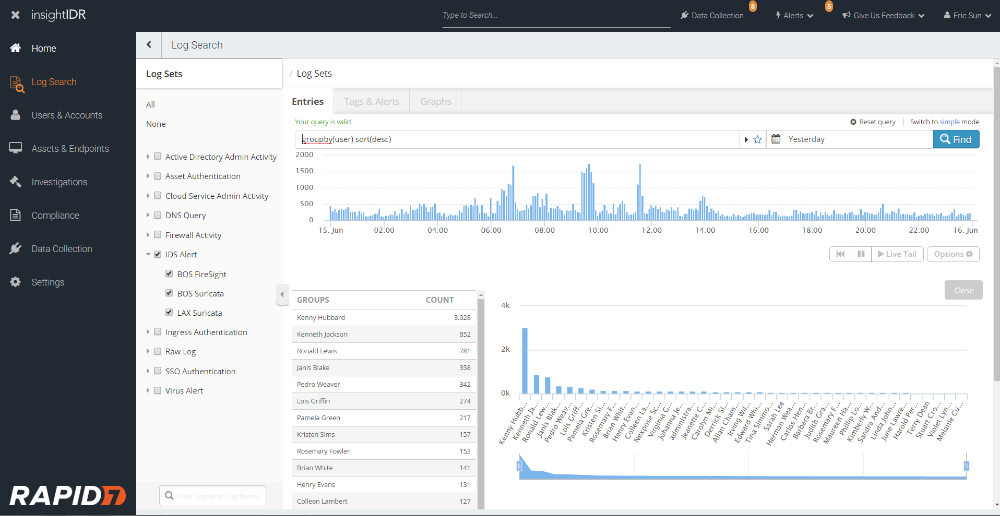
InsightIDR prioritizes where to hunt threats without a data degree. Traditional log search platforms waste time and money, requiring teams to manually retrace user activity across IP addresses, endpoints and cloud services. InsightIDR provides a complete record of relevant, contextualized behavior. No more writing queries or hiring certified data splunkers — InsightIDR reveals the answers hidden in user activity, logs, and endpoints.
About this category: Incident Response
The Cybersecurity Excellence Awards recognize incident response products and services. The category covers incident response platforms, retainers and response teams that contain attacks and restore operations.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
Related categories
View the category →How entries are judged →