RunSafe Security is purpose-built for embedded and legacy software environments where traditional security controls are difficult to deploy and patching is slow or operationally risky. Our platform is designed to give customers both (1) authoritative software supply chain visibility and (2) durable runtime exploit prevention, without requiring code rewrites, agents, or disruptive architecture changes.
Build-time SBOM (Embedded + C/C++): RunSafe generates SBOMs at build-time by observing file activity during compilation, producing an SBOM that reflects exactly what is included in the final build artifact, including static libraries and dependencies that are often missed. This approach reduces false positives/negatives common in source- and binary-based SBOM generation and is especially valuable for cross-compiled, long-lived embedded systems.
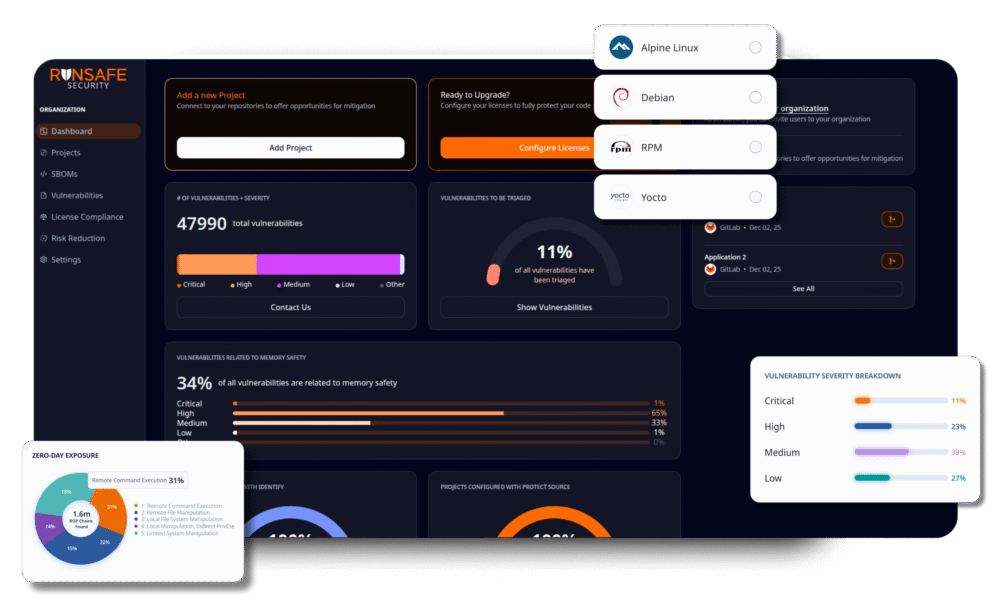
Security Platform Capabilities: After SBOM generation, customers can use the RunSafe Security Platform to manage SBOMs, identify known vulnerabilities (CVEs), verify open-source license compliance, perform reachability analysis, and prioritize remediation activities based on what actually ships in production.
Runtime Protection (Patented LFR): RunSafe Protect includes patented Load-time Function Randomization (LFR), a moving-target defense technique that randomizes software functions in memory each time the software runs. This prevents attackers from relying on predictable memory layouts, significantly increasing the difficulty of exploiting memory-based vulnerabilities such as buffer overflows. RunSafe’s protection is designed for embedded constraints: it preserves system behavior, adds no runtime performance overhead, and can be applied without rewriting application code, making it well-suited for OT and safety-critical systems.
About this category: Embedded Security
The Cybersecurity Excellence Awards recognize embedded security products. The category covers products that secure the software and hardware inside devices, such as secure boot, hardware roots of trust and runtime protection.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
Community Choice voting for the 2026 season closed on July 10, 2026.
What is the Community Choice Award?
A separate award decided by public vote, independent of the jury awards. Each completed share of a profile on LinkedIn, Facebook or X counted as one vote.
2027 award season
Nominations closeFebruary 27, 2027
Jury winners announcedWeek of March 22
Community Choice voting closesJuly 10, 2027
Nominate in this category
Enter a nomination in Embedded Security. Review takes about one business day.
Help This Nominee Win a Community Choice Award Vote by sharing this page:
24
Community
Votes
Cast your vote by sharing this nominee’s profile on LinkedIn, Facebook, or X, using the buttons above. Each completed social share adds one Community Choice vote.
Votes cast by July 10, 2027 will determine the Community Choice winners (independent of the jury awards). Winners will be announced before Black Hat USA.
What is the Community Choice Award? →
Community Choice is a separate award track from the jury-selected Cybersecurity Excellence Awards. Jury winners are chosen by expert judges, while Community Choice winners are determined by public voting. A nominee may be honored by the jury, the community, or both.