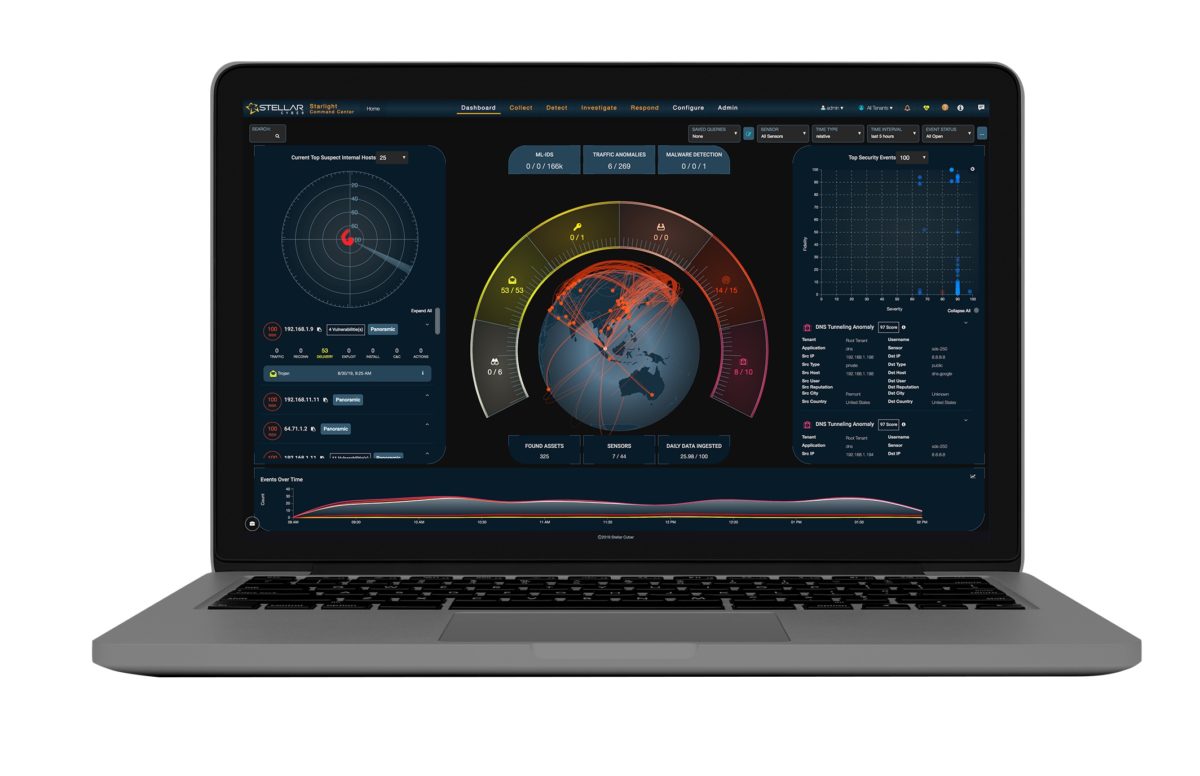
Open XDR is a cohesive security operations platform with many natively supported security tools while seamlessly integrating with third party tools. XDR typically locks in customers to a particular vendor’s tools, but Stellar Cyber developed the first Open XDR-powered security operations platform. In addition to its natively supported tools, it integrates with other popular security tools in the market, ingesting their data to retain investments and produce precise results through automatic event correlation. Stellar Cyber also uses a network of sensors to fill gaps and produce full visibility and fast understanding.
Open XDR fundamentally redefines how threat detection and response are done. It automatically collects, normalizes, enriches and correlates all security data from ANY security product into a single platform—with 360-degree visibility across through normalized and enriched metadata from ANY source—cloud, endpoints (including mobile devices), network, user, SaaS, email, applications and IoT. In short, analysts can use the Stellar Cyber console to identify, block and remediate complex cyberthreats across the entire attack surface.
Stellar Cyber gives security teams the power to identify the most important events in context without the extensive manual correlations needed with siloed security systems. It provides 360-degree visibility across the entire attack surface and enhances existing security tools. It minimizes alert fatigue, and weaker attack signals can be augmented with other data to ensure analysts see attack activities that would otherwise be under the radar.
Stellar Cyber is designed for organizations that are overworked and understaffed while need to better protect data and assets. The platform is horizontally applicable, since these conditions apply to most organizations. Stellar Cyber boosts the ability of a security team to find and stop attacks, eliminating or mitigating theft or damage.
How we are different
• Stellar Cyber is the only open XDR platform that seamlessly works with the existing tools and telemetry customers already own and trust with many built-in security tools. Open XDR retains customers’ existing cybersecurity investments by integrating with existing security products. It also eliminates other tools’ costs by natively supporting many of its own security tools.
• It provides a 360-degree view of the entire attack surface from network to endpoints, from applications to users by automatically correlate events across tools. Advanced attacks such as account takeovers and advanced persistence threats require many inputs to correctly connect the dots across the attack surface. Stellar Cyber combines threat intelligence, network data and log data to spot these complex attacks instantly. The platform delivers a single unified data lake and a single console for spotting and remediating complex attacks pieced together through auto-correlation.
• Signature based detections like IDS rules or Anti-virus, SIEM rules can detect known threats. But it fails to detect unknown or zero-day breaches beside too many false positives. Stellar Cyber has leveraged machine learning algorithms, both supervised and unsupervised including deep learning to detect attacks with high fidelity with the data collected from different tools. This dramatically reduces the detection time while improving security analysts’ efficiency.
About this category: Threat Detection and Response
The Cybersecurity Excellence Awards recognize products that detect and respond to threats across an organization. It is the broad detection category, for products that draw on several data sources or fit no narrower category.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
Community Choice voting for the 2021 season closed on July 10, 2021.
What is the Community Choice Award?
A separate award decided by public vote, independent of the jury awards. Each completed share of a profile on LinkedIn, Facebook or X counted as one vote.
2027 award season
Nominations closeFebruary 27, 2027
Jury winners announcedWeek of March 22
Community Choice voting closesJuly 10, 2027
Nominate in this category
Enter a nomination in Threat Detection and Response. Review takes about one business day.
Help This Nominee Win a Community Choice Award Vote by sharing this page:
6
Community
Votes
Cast your vote by sharing this nominee’s profile on LinkedIn, Facebook, or X, using the buttons above. Each completed social share adds one Community Choice vote.
Votes cast by July 10, 2027 will determine the Community Choice winners (independent of the jury awards). Winners will be announced before Black Hat USA.
What is the Community Choice Award? →
Community Choice is a separate award track from the jury-selected Cybersecurity Excellence Awards. Jury winners are chosen by expert judges, while Community Choice winners are determined by public voting. A nominee may be honored by the jury, the community, or both.
2021 winners in Threat Detection and Response
To keep judging fair, each entry is judged against peers in its segment, so a category can have more than one Gold winner.