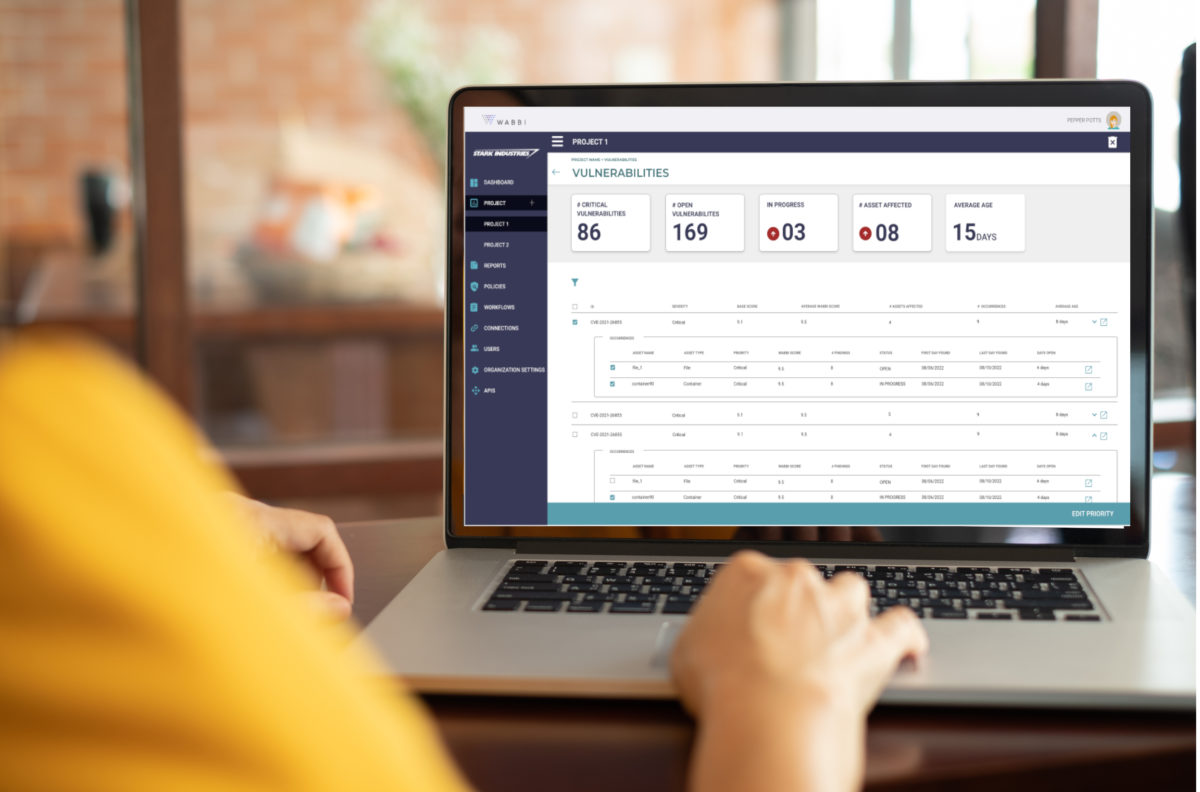
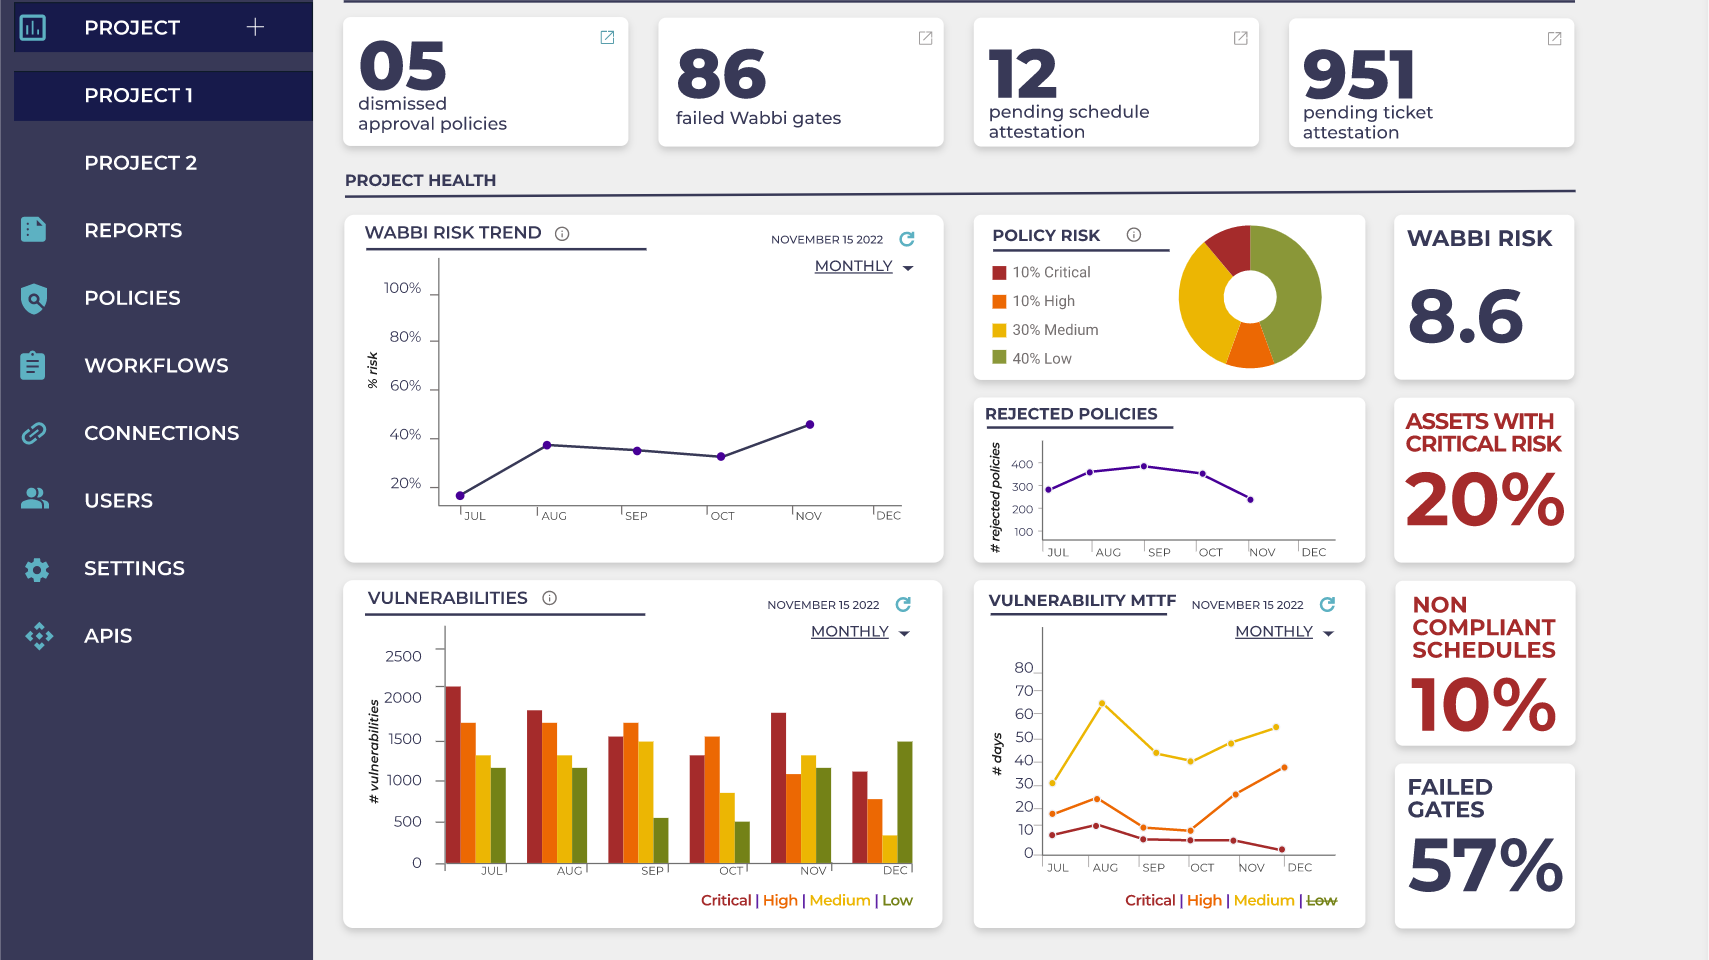
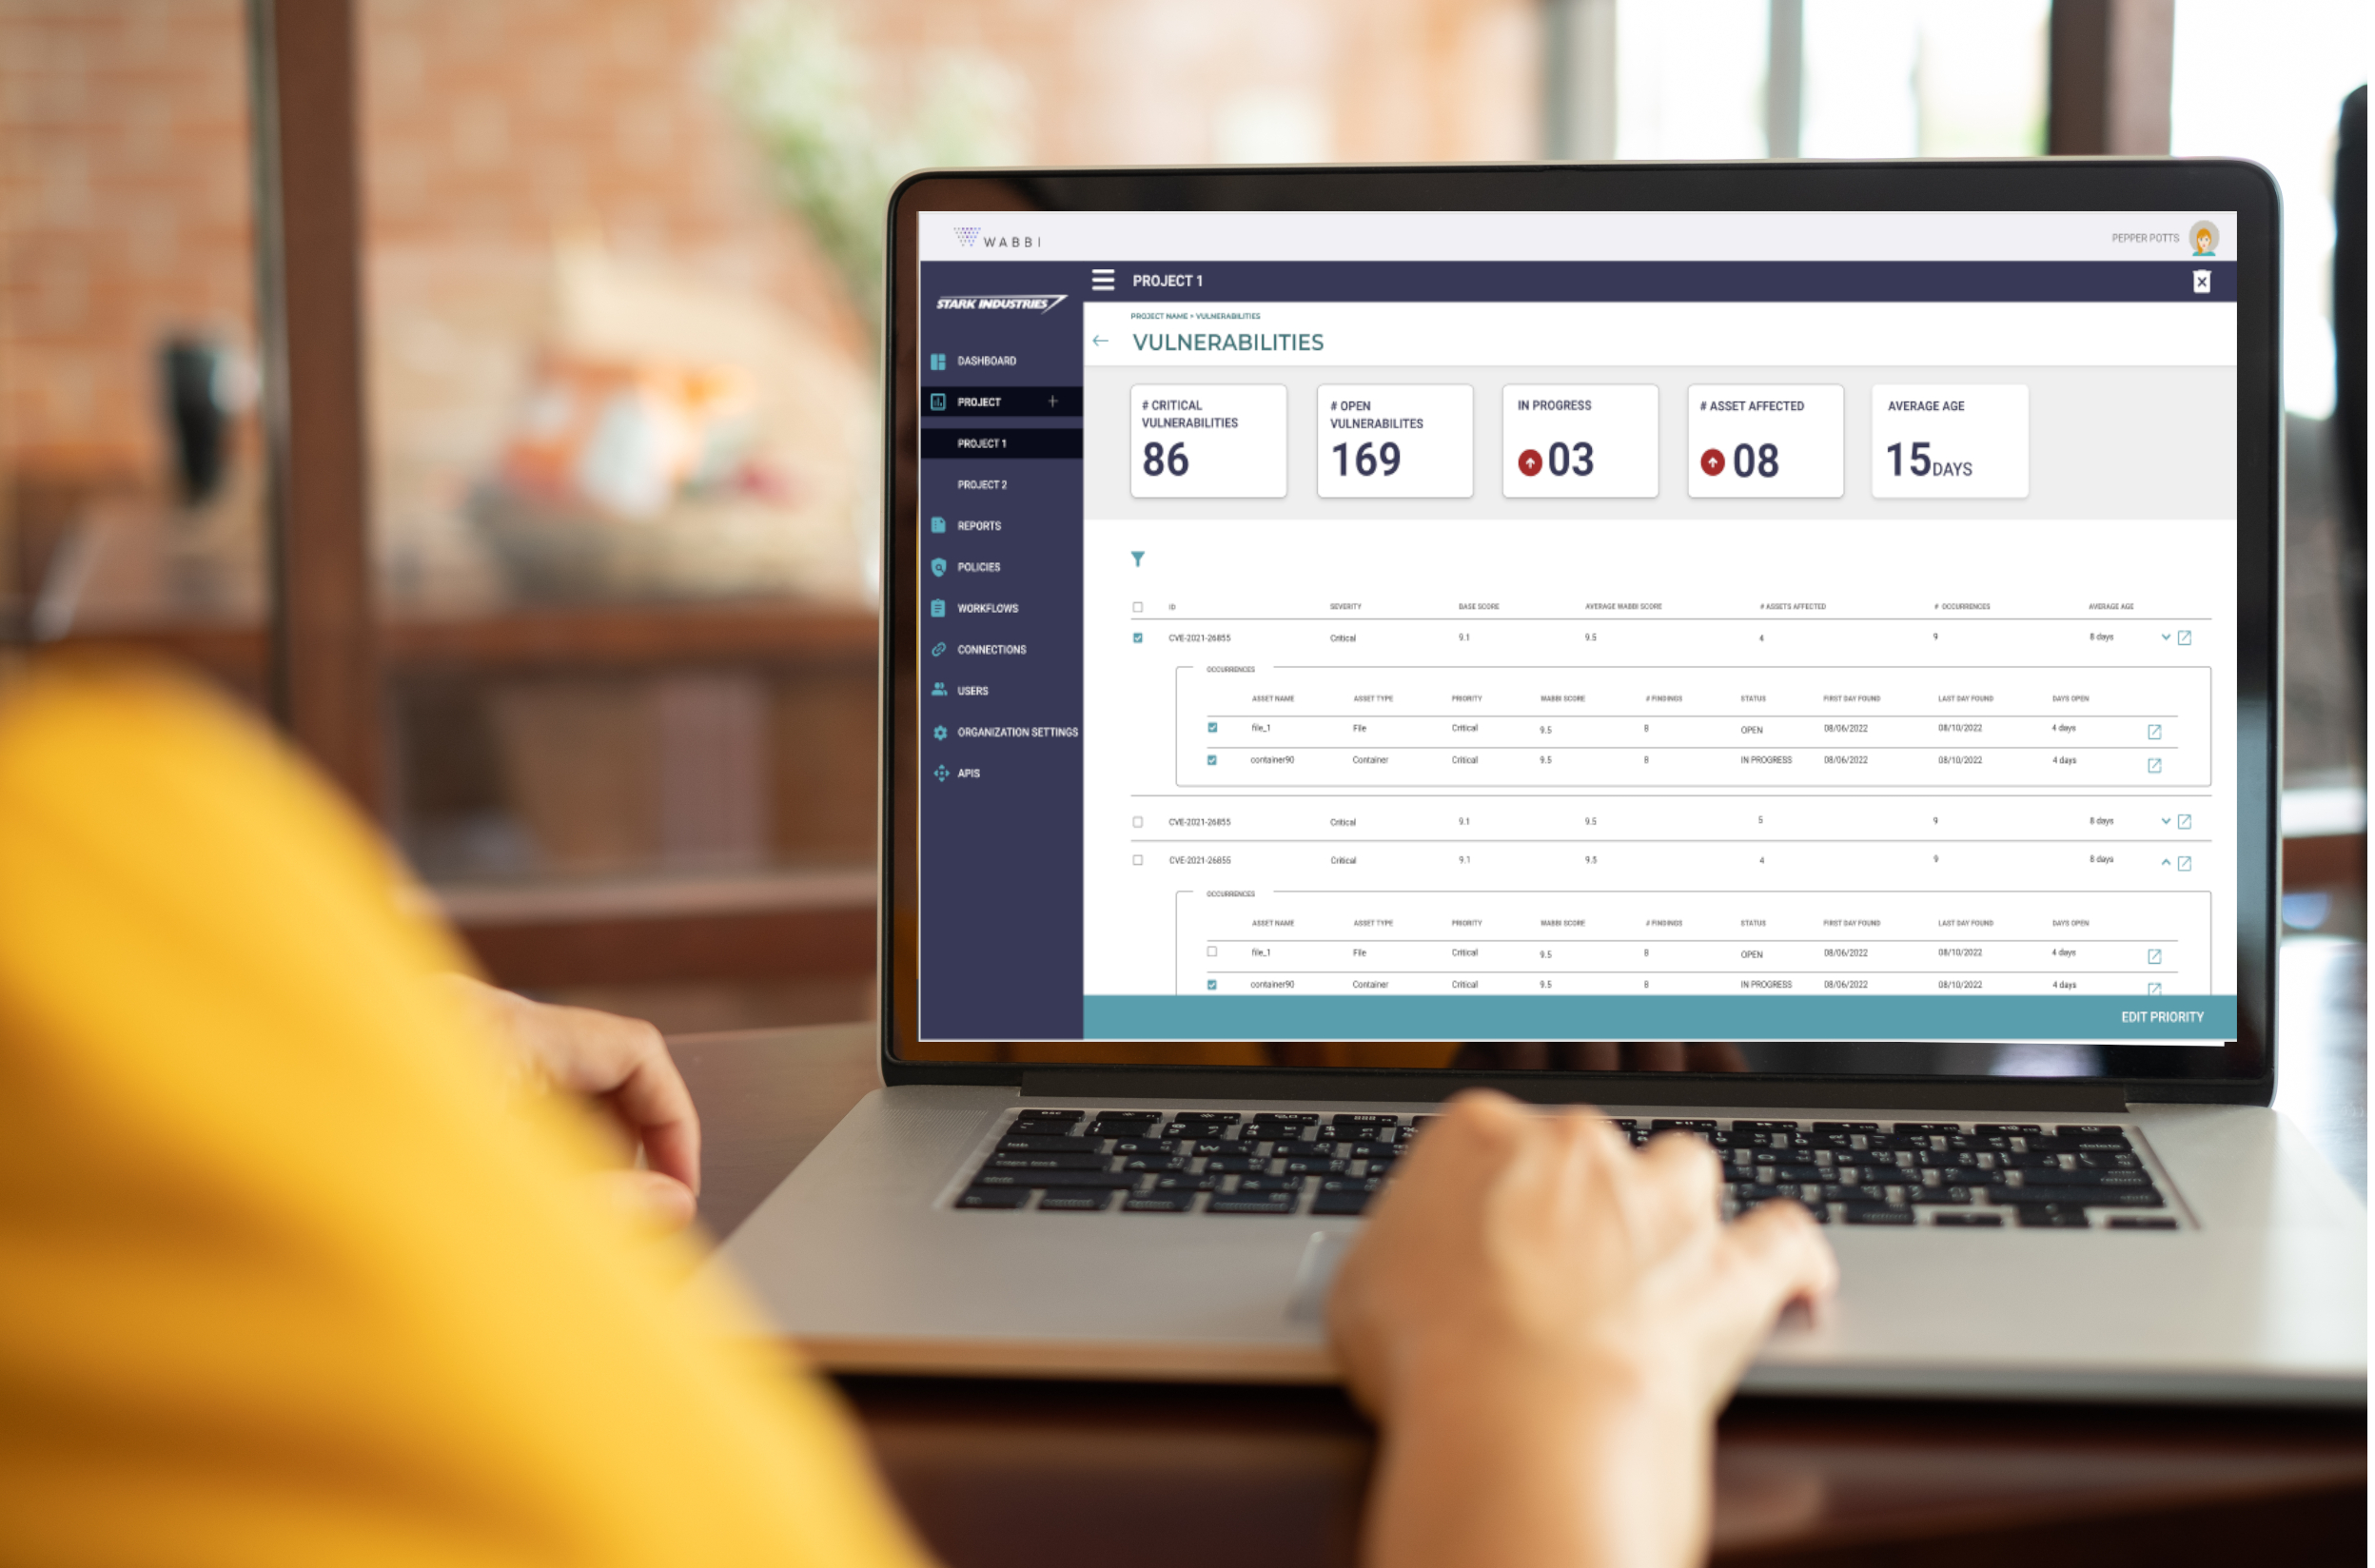
Wabbi’s continuous security platform orchestrates and correlates all components of an application security program to bridge the gap between security and development. By analyzing existing product design architecture and security policies, Wabbi enables context-based management of application security enabling its end-to-end integration into the complete software development lifecycle, and ongoing dynamic management of it in real-time in responses to changes both in security requirements and at the application layer. This enables transparency in and prioritization of the security activities and remediation, with closed loop-integrations to reduce noise in existing security and development workflows.
How we are different
- Wabbi has defined the market of Application Security Orchestration and Correlation so enterprises can simplify the complexity of integrating security and development. The promise of DevSecOps has failed to be realized due to one-sided, point-solution based efforts that fail to marry the Security and DevOps processes which is required to integrate AppSec in the SDLC. While DevSecOps has been discussed for the better part of a decade, Wabbi is finally enabling its promise to be realized with its industry leading platform and will lead the DevSecOps revolution.
- As the only true application security platform that enables not just integration, but interoperability between Security & Development environments, Wabbi provides a full-stack view of the application security posture from asset risk to policy compliance. Traditional approaches and point solutions in the market fail to capture this which means they are not providing an accurate assessment of the application risk posture because they don’t have the whole picture. Wabbi goes as afar as to understand the asset relationships and rules – even for unscanned assets.
- Wabbi goes beyond benefiting an organization by reducing the risk of breach through more effective Application Security. It has hard ROI on the bottom line as it reduces project delivery delay, increases developer productivity, and enables exponential scaling of the AppSec team without a single additional FTE.
About this category: DevSecOps
The Cybersecurity Excellence Awards recognize DevSecOps products. The category covers products that build security into software development, such as security testing in build pipelines and guidance for developers.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
Community Choice voting for the 2023 season closed on July 10, 2023.
What is the Community Choice Award?
A separate award decided by public vote, independent of the jury awards. Each completed share of a profile on LinkedIn, Facebook or X counted as one vote.
2027 award season
Nominations closeFebruary 27, 2027
Jury winners announcedWeek of March 22
Community Choice voting closesJuly 10, 2027
Nominate in this category
Enter a nomination in DevSecOps. Review takes about one business day.
Help This Nominee Win a Community Choice Award Vote by sharing this page:
6
Community
Votes
Cast your vote by sharing this nominee’s profile on LinkedIn, Facebook, or X, using the buttons above. Each completed social share adds one Community Choice vote.
Votes cast by July 10, 2027 will determine the Community Choice winners (independent of the jury awards). Winners will be announced before Black Hat USA.
What is the Community Choice Award? →
Community Choice is a separate award track from the jury-selected Cybersecurity Excellence Awards. Jury winners are chosen by expert judges, while Community Choice winners are determined by public voting. A nominee may be honored by the jury, the community, or both.
Also recognized in DevSecOps, 2023
To keep judging fair, each entry is judged against peers in its segment, so a category can have more than one Gold winner.