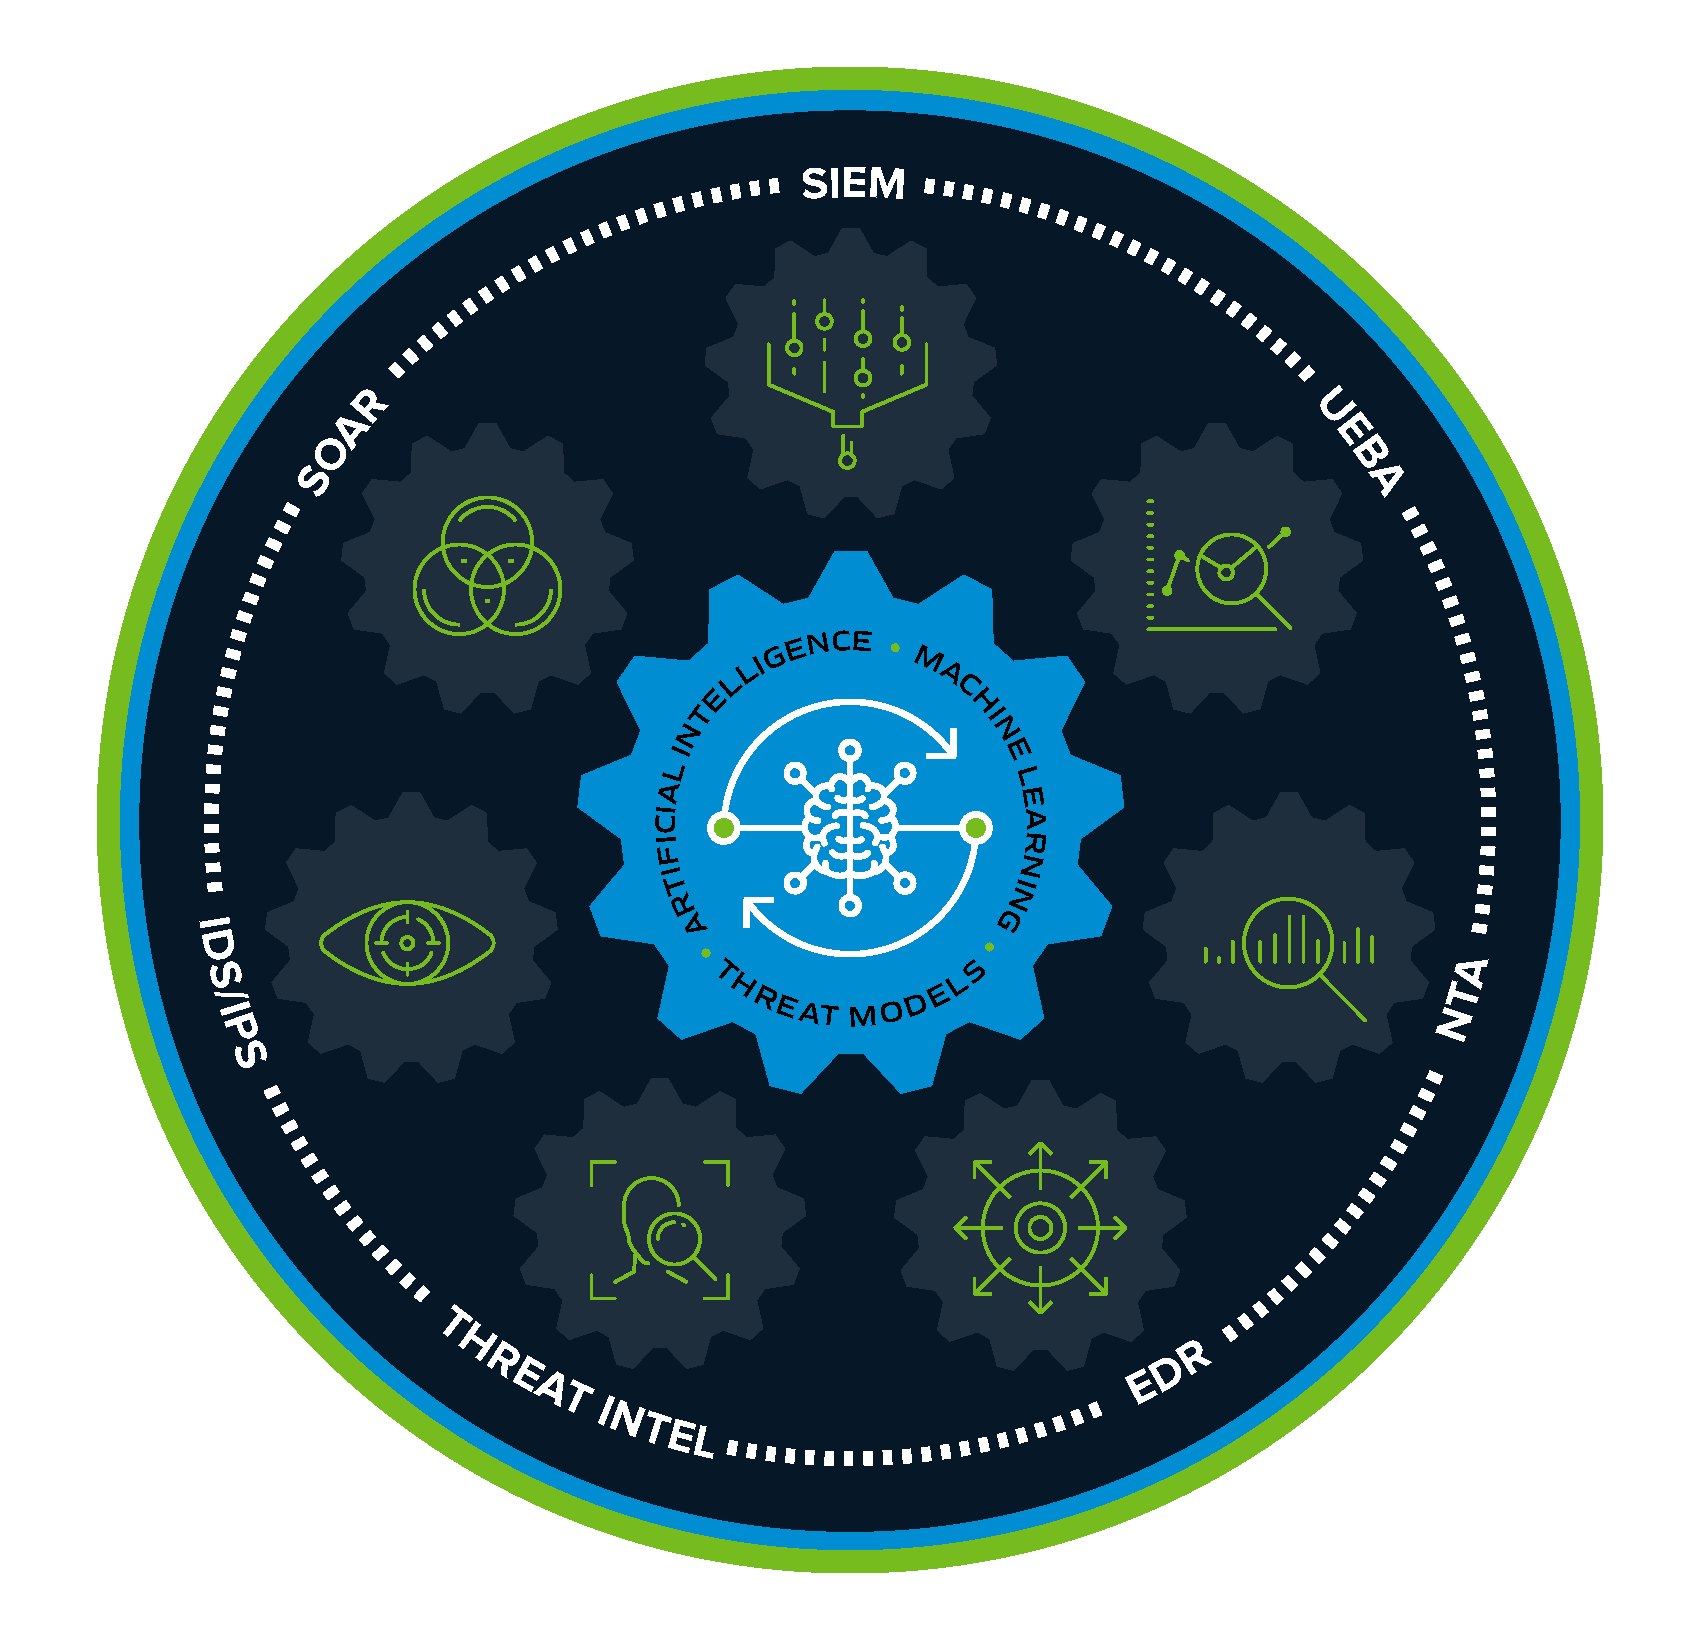
ARIA Advanced Detection and Response (ADR) is a fully automated, AI-SOC solution purpose-built with the capabilities of seven security tools — including SIEMs, IDS/IPSs, EDRs, Threat Intel tools, NTAs, UEBAs, and SOARs.
ARIA ADR’s 60+ machine learning-powered threat models, guided by AI, can find, stop and remediate the most harmful threats (including ransomware, malware, APTs, DDoS, intrusions, insider threats, network policy enforcements and data exfiltrations) in real-time and with no manual intervention required. This is a powerful advantage over most traditional security operation approaches that surface more noise than threats and require highly-trained security operations staff.
With this single, comprehensive solution organization’s will no longer have to settle for limited threat surface coverage or struggle to integrate and maintain disparate tools at substantial cost and little return.
With ARIA ADR, organizations will improve their overall security posture, across the entire enterprise – premises, data centers, and cloud instances. In just one solution, ARIA ADR exceeds the performance of seven security tools and is also 90% less cost, requires 1/100 of the manpower demanded of a traditional SOC, and 100% automation capable.
How we are different
ARIA ADR Provides the Industry's Best ROI for Threat Detection and Response:
- Uses powerful AI capabilities to significantly reduce noise and present only validated and actionable threat alerts.
- Covers the entire environment – on-premises systems, IoT devices, and cloud-based systems - and it also enforces network connectivity policies.
- Combines the capabilities of seven disparate tools into a single platform.
- Organizations gain a complete AI-SOC at a fraction of the cost, right out of the box.
- Automation replaces costly manual identification, verification and remediation
- Identify the threats that are normally missed, in real-time, while they are still early in the kill chain—before they can inflict significant harm.
- ML-based threat models replace time-consuming signature-based rules creation
About this category: Threat Detection and Response
The Cybersecurity Excellence Awards recognize products that detect and respond to threats across an organization. It is the broad detection category, for products that draw on several data sources or fit no narrower category.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
Community Choice voting for the 2021 season closed on July 10, 2021.
What is the Community Choice Award?
A separate award decided by public vote, independent of the jury awards. Each completed share of a profile on LinkedIn, Facebook or X counted as one vote.
2027 award season
Nominations closeFebruary 27, 2027
Jury winners announcedWeek of March 22
Community Choice voting closesJuly 10, 2027
Nominate in this category
Enter a nomination in Threat Detection and Response. Review takes about one business day.
Help This Nominee Win a Community Choice Award Vote by sharing this page:
6
Community
Votes
Cast your vote by sharing this nominee’s profile on LinkedIn, Facebook, or X, using the buttons above. Each completed social share adds one Community Choice vote.
Votes cast by July 10, 2027 will determine the Community Choice winners (independent of the jury awards). Winners will be announced before Black Hat USA.
What is the Community Choice Award? →
Community Choice is a separate award track from the jury-selected Cybersecurity Excellence Awards. Jury winners are chosen by expert judges, while Community Choice winners are determined by public voting. A nominee may be honored by the jury, the community, or both.
2021 winners in Threat Detection and Response
To keep judging fair, each entry is judged against peers in its segment, so a category can have more than one Gold winner.