Nipper is trusted by US military and civilian federal agencies and their prime and sub-contractors to accurately analyze network devices against trusted risk management and control frameworks, and is available as an offline configuration review tool, enabling the assessment of air-gapped networks.
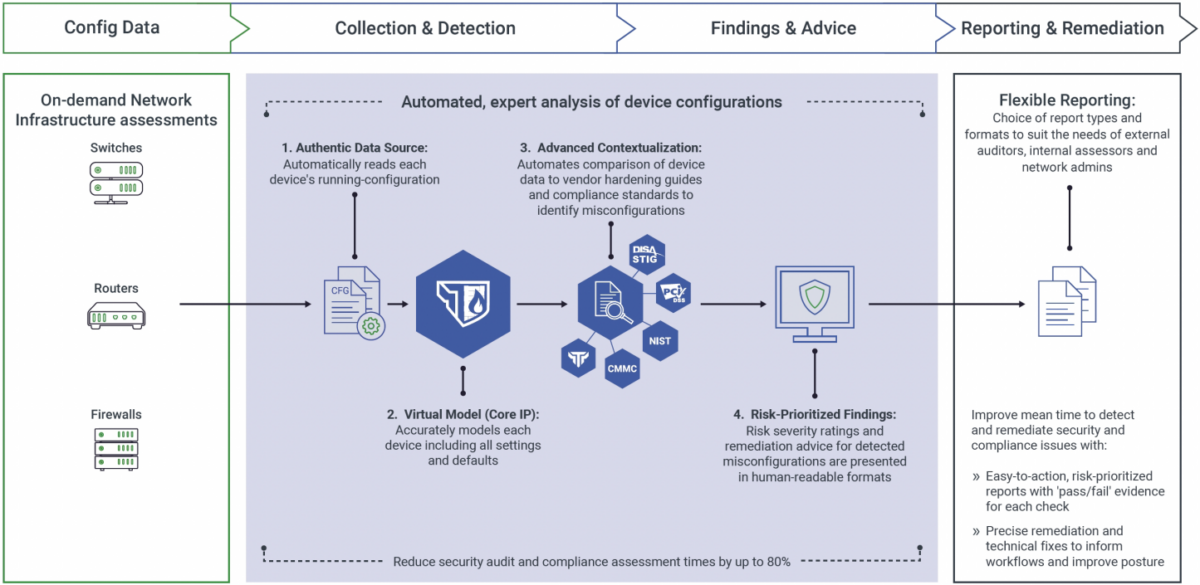
By virtually modelling device configurations as single entities to consider interdependencies across the network, Nipper accurately detects vulnerabilities in routers, switches and firewalls, by providing evidence-based compliance reporting for risk management frameworks including STIGs, NIST SP 800-53 and PCI DSS 4.0, and exception-based security reporting for CIS Benchmarks, NIST SP 800-171, and CMMC.
Nipper automatically prioritizes findings by security and/or compliance risk and provides risk remediation advice with exact technical fixes for misconfigurations, to further support and accelerate the process of customers becoming secure and compliant. Nipper helps customers reduce MTTD vulnerabilities, as well as MTTR, in order to reduce their exposure to critical risks.
As part of the assessment phase for Zero Trust maturity, Nipper can also help assess the compliance state of routers, switches and firewalls, discovering any vulnerabilities, identifying where configurations drift away from a secure and compliant state, and recommending how to mitigate the risk to improve the compliance posture of the network.
Nipper’s accuracy-advantage has proven to reduce audit times by up to 80% as a result of not wasting time investigating false positives. Delivering the accuracy in configuration assessment that is critical to the security of network devices, Nipper has been helping NOCs and SOCs build operational confidence in threat detection and management for over a decade. The software’s accuracy-advantage and trusted risk criticality rating have made it a must-have tool for organizations and CNI leaders around the world, including the UK Ministry of Defence, Aldi, Deloitte and US Department of Defense.
About this category: Cybersecurity Assessment
The Cybersecurity Excellence Awards recognize cybersecurity assessment products and services. The category covers risk and maturity assessments, gap analyses, audits and one-off penetration tests that show where an organization’s security stands.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
Related categories
View the category →How entries are judged →