In 2016, Recorded Future spearheaded the charge to empower every organization with relevant threat intelligence they can apply across their whole security infrastructure.
Our OMNI Intelligence Partner program was launched. Seeing security teams maximize their value from Recorded Future through all-source analysis that combines our unmatched breadth of intelligence with specialized threat content. Partnering with top security firms to give analysts a breakthrough in speed and confidence for this all-source analysis. Launch partners included Palo Alto Networks, Resilient, FireEye iSIGHT Intelligence, DomainTools, Farsight Security, PhishMe ReversingLabs, and Shodan. Security teams get on-demand integration of malware sandbox analysis, incident response investigations, and finished intelligence reporting, as well as domain, DNS, phishing, and internet of things (IoT) enrichment — all put in context with Recorded Future’s real-time threat intelligence.
We also made real-time, high context threat intelligence available to security operations teams through their SIEM. Our integrations let them correlate data in their SIEM with intelligence from Recorded Future. Our IP address risk list identifies thousands of indicators, and gives them dozens of context features to target the indicators that matter most for their security. It’s not just an IP list with risk scores; we continually update and age out indicators with patented algorithms that mine risk evidence from hundreds of thousands of sources including technical feeds, social media, security communities, dark web, paste sites and code repositories.
How we are different
Our customers are gaining measurable value from our real-time threat intelligence. Here are three metrics reported by our customers:
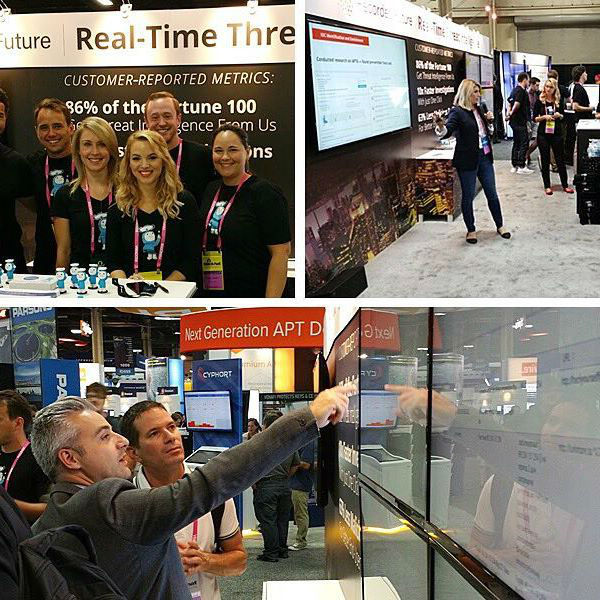
86% of the Fortune 100 uses Recorded Future
10x Productivity Gain From Real-Time Threat Intelligence for SIEMs
63% reduction in malicious traffic
About this category: Most Innovative Cybersecurity Company
The Cybersecurity Excellence Awards recognize cybersecurity companies for innovation that customers have put to use. The award covers companies of any size that brought new technology, a new approach or a new product category to the market.
An independent jury of security practitioners, analysts and CISOs scores each nomination on leadership, innovation and impact. Each nomination competes in its category against organizations of similar size and region. Entry packages, sponsorship and public votes do not affect the jury's scores.
A separate award decided by public vote, independent of the jury awards. Each completed share of a profile on LinkedIn, Facebook or X counted as one vote.
2027 award season
Nominations closeFebruary 27, 2027
Jury winners announcedWeek of March 22
Community Choice voting closesJuly 10, 2027
Nominate in this category
Enter a nomination in Most Innovative Cybersecurity Company. Review takes about one business day.
Help This Nominee Win a Community Choice Award Vote by sharing this page:
6
Community
Votes
Cast your vote by sharing this nominee’s profile on LinkedIn, Facebook, or X, using the buttons above. Each completed social share adds one Community Choice vote.
Votes cast by July 10, 2027 will determine the Community Choice winners (independent of the jury awards). Winners will be announced before Black Hat USA.
What is the Community Choice Award? →
Community Choice is a separate award track from the jury-selected Cybersecurity Excellence Awards. Jury winners are chosen by expert judges, while Community Choice winners are determined by public voting. A nominee may be honored by the jury, the community, or both.
Also nominated in Most Innovative Cybersecurity Company, 2017